Objective
Build a realistic blue-team lab where a domain workstation requests a Kerberos service ticket for an SPN-backed service account, then trace useful activity across the endpoint, domain controller, and SIEM.
BLUE TEAM · DETECTION ENGINEERING
Active Directory + Wazuh SIEM
Build a realistic blue-team lab where a domain workstation requests a Kerberos service ticket for an SPN-backed service account, then trace useful activity across the endpoint, domain controller, and SIEM.
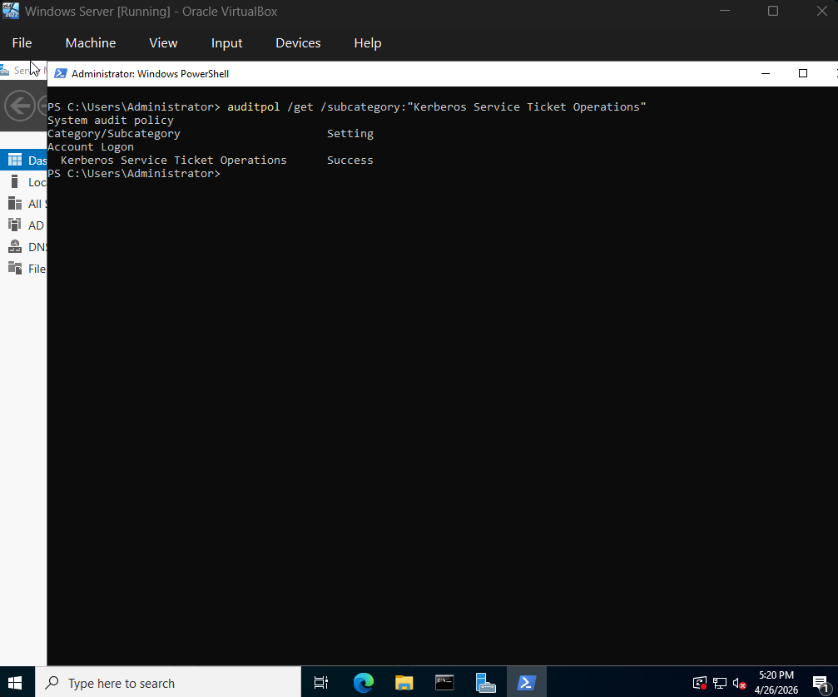
1 · Audit policy
Kerberos Service Ticket Operations auditing enabled on dc01 via Group Policy; the policy is associated with Event ID 4769.
2 · SIEM telemetry
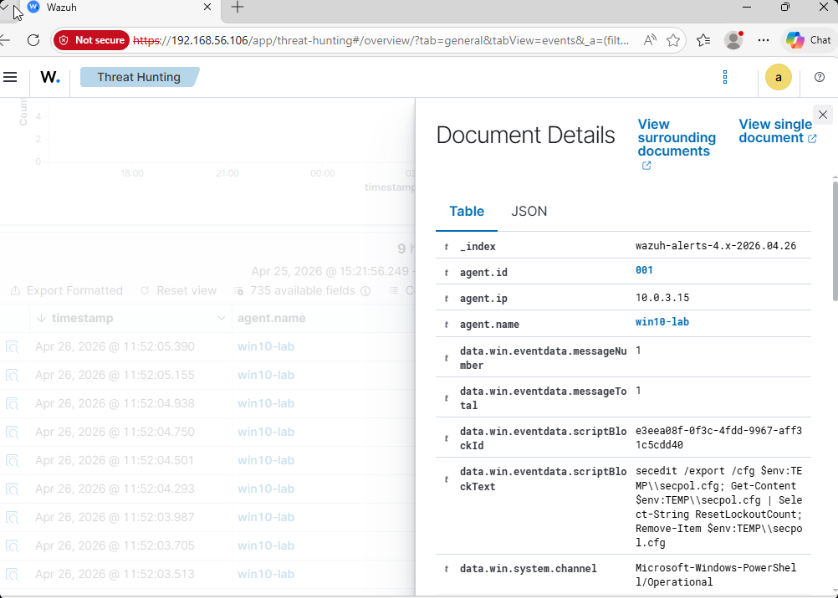
PowerShell Script Block Logging (Event ID 4104) from win10-lab ingested and reviewed in the Wazuh Threat Hunting dashboard.
3 · Process evidence
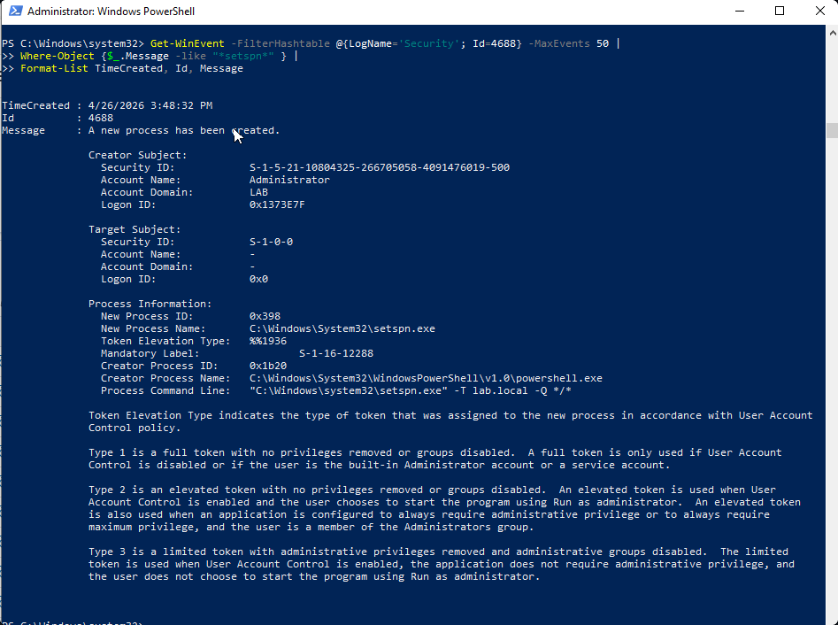
Event ID 4688 records setspn.exe -T lab.local -Q */* spawned from PowerShell for SPN enumeration in the lab.
Click a screenshot to view it full size.
Enabled Kerberos and endpoint auditing, routed PowerShell telemetry to Wazuh, and validated the investigation trail against the source Windows logs.
Tools: Wazuh · Active Directory · Windows Event Logging · PowerShell · VirtualBox
This project was conducted in an isolated learning environment. Screenshots retain lab-only hostnames and private network addresses.