Objective
Simulate PowerShell Remoting from a domain workstation to a Windows Server domain controller, then investigate the activity from a defender’s perspective using Windows event logs and Wazuh.
BLUE TEAM · DETECTION ENGINEERING
Active Directory + Wazuh SIEM
Simulate PowerShell Remoting from a domain workstation to a Windows Server domain controller, then investigate the activity from a defender’s perspective using Windows event logs and Wazuh.
1 · Remote execution
Used Invoke-Command from win10-lab to run whoami, hostname, and ipconfig on dc01.
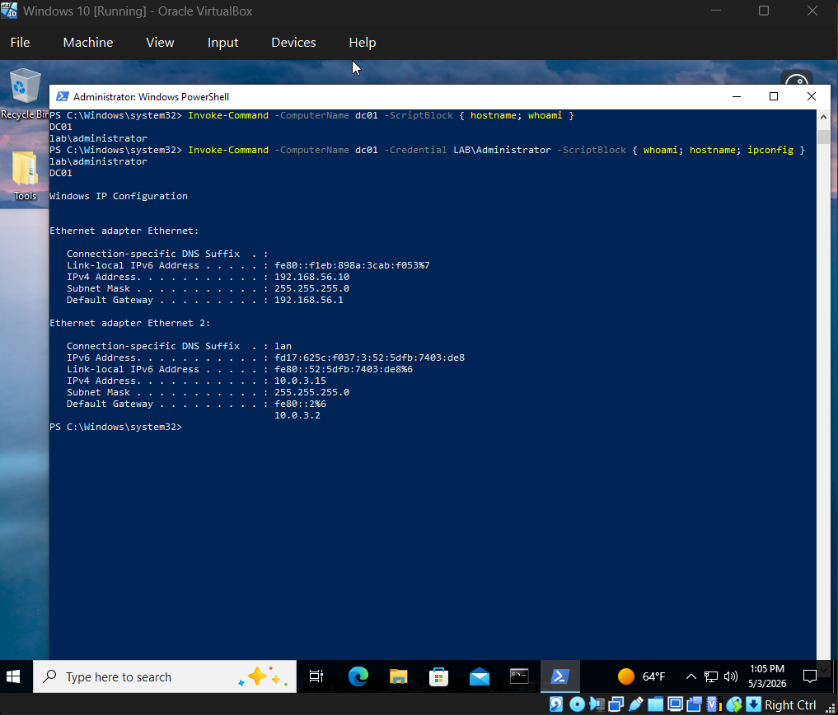
2 · Script block event
Confirmed locally that PowerShell logging captured the remote command under Event ID 4104.
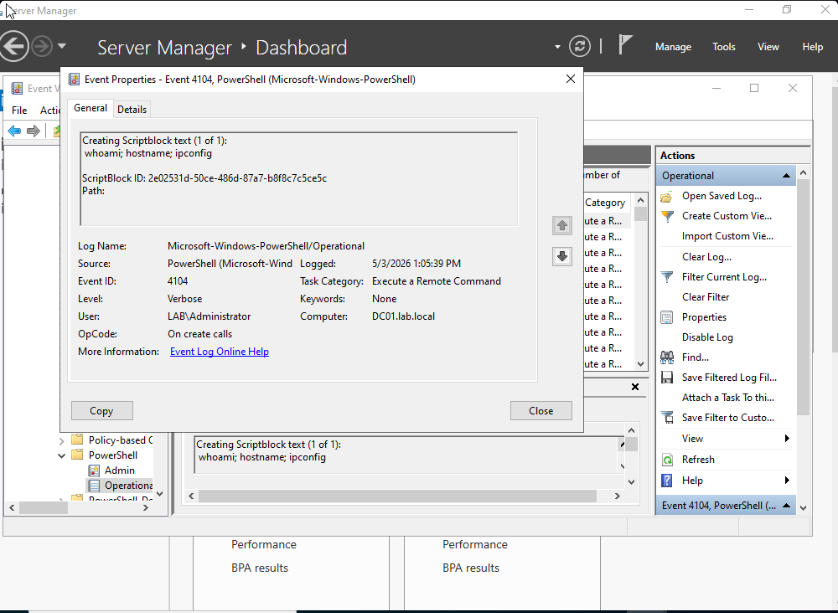
3 · SIEM investigation
Queried Wazuh for Event ID 4104 from dc01 and reviewed the PowerShell script block in the Threat Hunting view.
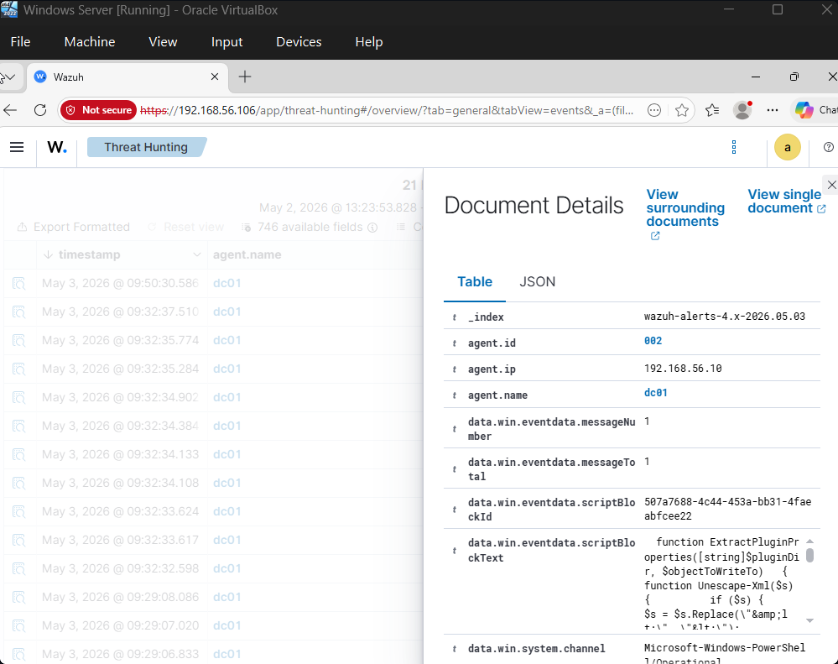
Click a screenshot to view it full size.
Enabled PowerShell Remoting, verified WinRM connectivity with Test-WSMan, executed a remote command, then confirmed its script block in Windows Event Viewer and Wazuh.
Enabled PowerShell Remoting on the workstation and domain controller; checked connectivity to dc01 with Test-WSMan.
Ran Invoke-Command remotely to collect the hostname, user context, and network configuration from the domain controller.
Reviewed Event ID 4104 locally, then searched Wazuh using agent.name:dc01 AND data.win.system.eventid:"4104".
Tools: PowerShell Remoting · Windows Event Logging · Wazuh · Active Directory
Conducted in an isolated learning environment. Screenshots show lab-only hostnames and private IP addresses.